Enforce authority. Inspect the result.
The Trust plane specifies deterministic policy, native ActionRisk, approvals, and evidence at each boundary. Your implementation checks current owned mandates and every delegation ancestor, binds approvals to the complete action and release, and enforces active isolation, credentials and data paths. Traces support evaluation and replay; they do not establish permission or prove success without the required outcome evidence.
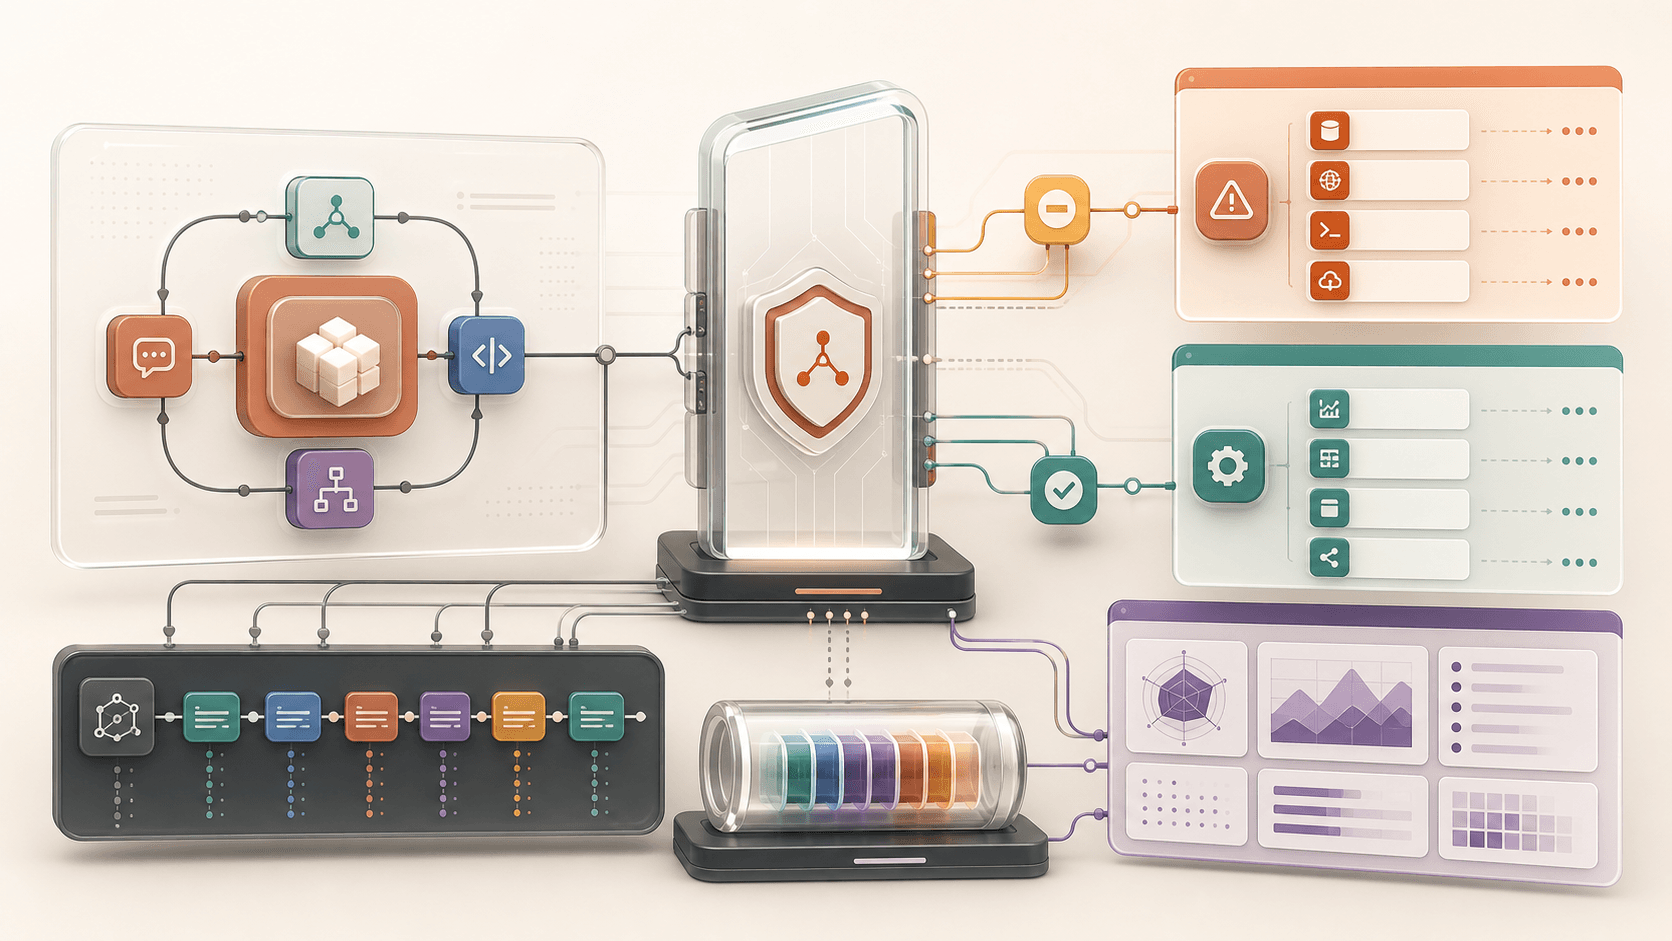
Policy, approvals, evaluation, traces, and replay sit outside model code, with independently enforced action boundaries in your implementation.
- 01Policy Engine
Evaluates rules at compiler, critic, and tool boundaries.
- 02ActionRisk
Evaluate effect, authority, reversibility, interaction, and data scope independently.
- 03Identity
Checks current owner, tenant, audience, delegation ancestry and revocation.
- 04Evaluators
Score safety, utility, cost, latency, and compliance.
- 05Replay record
Keeps eligible bounded evidence and declared replay properties.
Native risk, compatible modes
ActionRisk is the native multidimensional model. read_only, local_write, network, delegated, and destructive remain the v1 projection and safety ceiling.
Failure to prevent
Model self-policing: security must not depend on the model. The Policy Engine is the deterministic decision source. Independent gateways enforce current permission; a model Critic cannot authorize dispatch.
evaluators
Policy compliance · Utility · Latency · Safety · Economics. Tracked per intent, per tenant, per pack version; complete positive, negative, fault and utility evidence must support each exact workflow, implementation, release and environment. Missing evidence is not a pass.
Policy bundle (JsonLogic) outside agent code
Policy is authored, versioned, and evaluated at the boundary; a deployment may also require supply-chain signatures. The compiler evaluates applicable predicates deterministically and stops on a structured expression error. Business-rule priority cannot override mandatory guardrails, native risk, current authority or approval obligations. This legacy rule fragment describes a requirement; it does not grant permission or redeem an approval.
The effect gateway independently binds nested arguments, evidence, actor, tenant, native risk, monetary amount and currency, policy, profile and release. It verifies the current entitled approval quorum and active boundary, then uses atomic ownership, fencing and original shared budget reservations. Unknown provider outcomes require reconciliation; cancellation cannot erase effects or spent capacity. Data rules cover all nine processing stages and actual recipients. See the execution contract, exact control profiles and conformance evidence. This repository supplies deterministic references, not a deployed policy or sandbox service.
{
  "rule_id": "R_HIGH_VALUE_REQUIRES_APPROVAL",
  "applies_to": { "intent": "support.refund" },
  "if": {
    "and": [
      { "==": [{ "var": "user.role" }, "support_agent"] },
      { ">": [{ "var": "request.context.refund_amount" }, 3000] }
    ]
  },
  "then": {
    "allow": true,
    "approval_mode": "destructive",
    "requires_approval_gate": "GATE_FINANCE_APPROVAL",
    "arg_constraints": { "currency": { "enum": ["INR"] } }
  },
  "decision_binding": "support.refund.execute"
}