Bound execution and verify completion
Planner, Executor, and Critic are responsibilities in the canonical bounded loop. They do not require three deployed agents. Start with one workflow, verified steps, and an explicit acceptance check. Add delegation or durable execution when tested needs justify the topology. Every applicable control remains mandatory before dependent work: current owned and ancestor authority, exact approval/quorum, active containment/credentials/data and provider preconditions.
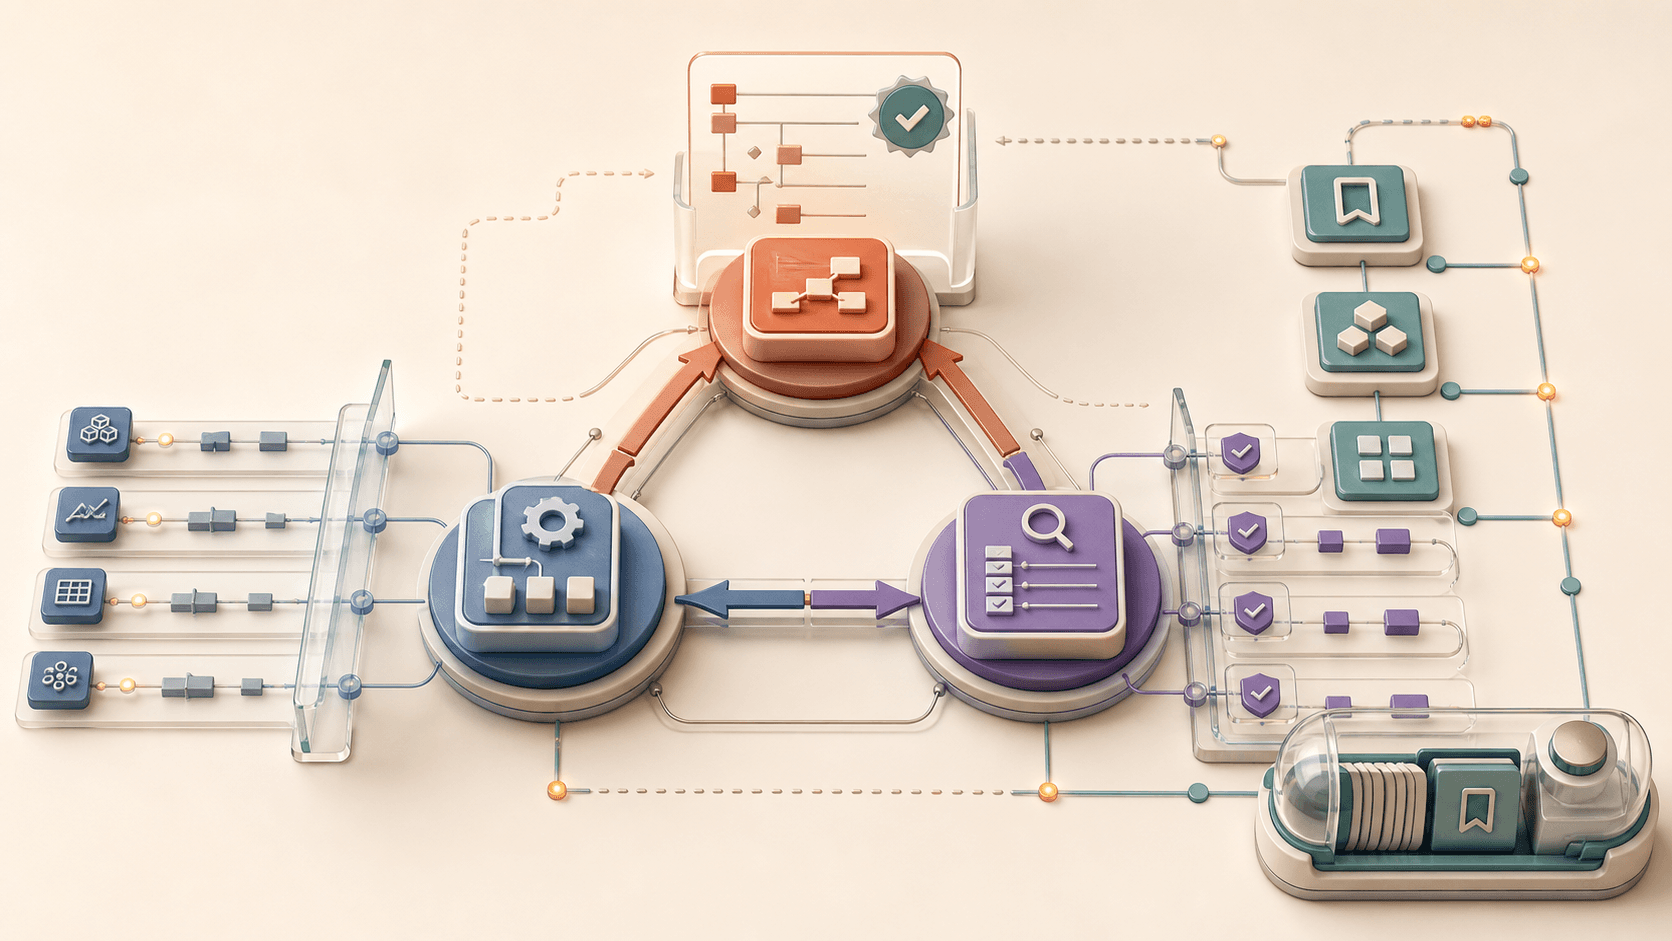
Planner, Executor and Critic are responsibilities; protected state, current authority and observed effects govern continuation.
- 01Planner
Produces typed steps, dependencies, and declared risk.
- 02Critic verify
Challenges plans; independent gateway checks enforce actual authority and boundaries.
- 03Executor
Runs verified steps only through approved tool envelopes.
- 04Critic score
Assesses evidence; unknown effects require provider reconciliation before unsafe retry.
- 05Checkpoint
Protects run identity, current ownership and original spent/reserved capacity.
Three roles, three artifacts
Plan, transcripts and verdicts need trusted collection. Offline replay compares deterministic artifacts exactly and model-dependent judgments through declared properties, with live effects disabled.
Failure to test
Unenforced responsibilities: a single agent can preserve clear boundaries, while several agents can share the same blind spot. Model agreement cannot replace current controls or independent effect evidence.
Metrics that matter
Plan-verification pass rate, retry/recovery rate, escalation rate by risk tier, mean time to safe completion, loop-guard trip rate.
Typed plan with decision checkpoints
This illustrative plan carries steps, dependencies, native action-risk declarations, a v1 compatibility mode, and decision checkpoints that resolve to a Decision Spec from the Decision Catalog. Plan is an orchestration application design here, not a separately published canonical schema. A gate name or mode does not authorize a call; the runtime binds the complete actual action to current stored approval and entitled independent quorum.
Protected atomic run/operation/approval/budget stores and target-enforced generation fences govern wake/resume. All child, review, retry and repair work shares original limits; unknown provider outcomes retain stable identity/reservations. Cancellation and tuple rollback cannot prove stop or reversal. Govern all nine data stages and derived copies. Read the durable execution contract, choose exact profiles and collect current useful, denial and fault evidence for the actual deployment. No scheduler, store or dispatcher is operated by this page.
{
  "plan_id": "plan_refund_01",
  "intent": "support.refund",
  "steps": [
    { "id": "s1", "tool": "adp_orders.lookup", "params": { "order_id": "ord_881" } },
    { "id": "s2", "tool": "adp_policy.eval", "depends_on": ["s1"] },
    {
      "id": "s3",
      "tool": "adp_payments.issue_refund",
      "depends_on": ["s2"],
      "action_risk": {
        "effect": "external_state",
        "authority": "human_approved",
        "reversibility": "compensatable",
        "interaction": "api",
        "data_scope": "CONFIDENTIAL"
      },
      "approval_mode": "destructive",
      "requires": ["GATE_FINANCE_APPROVAL"]
    }
  ],
  "decision_checkpoints": [
    { "decision_id": "support.refund.execute", "after_step": "s2" }
  ]
}